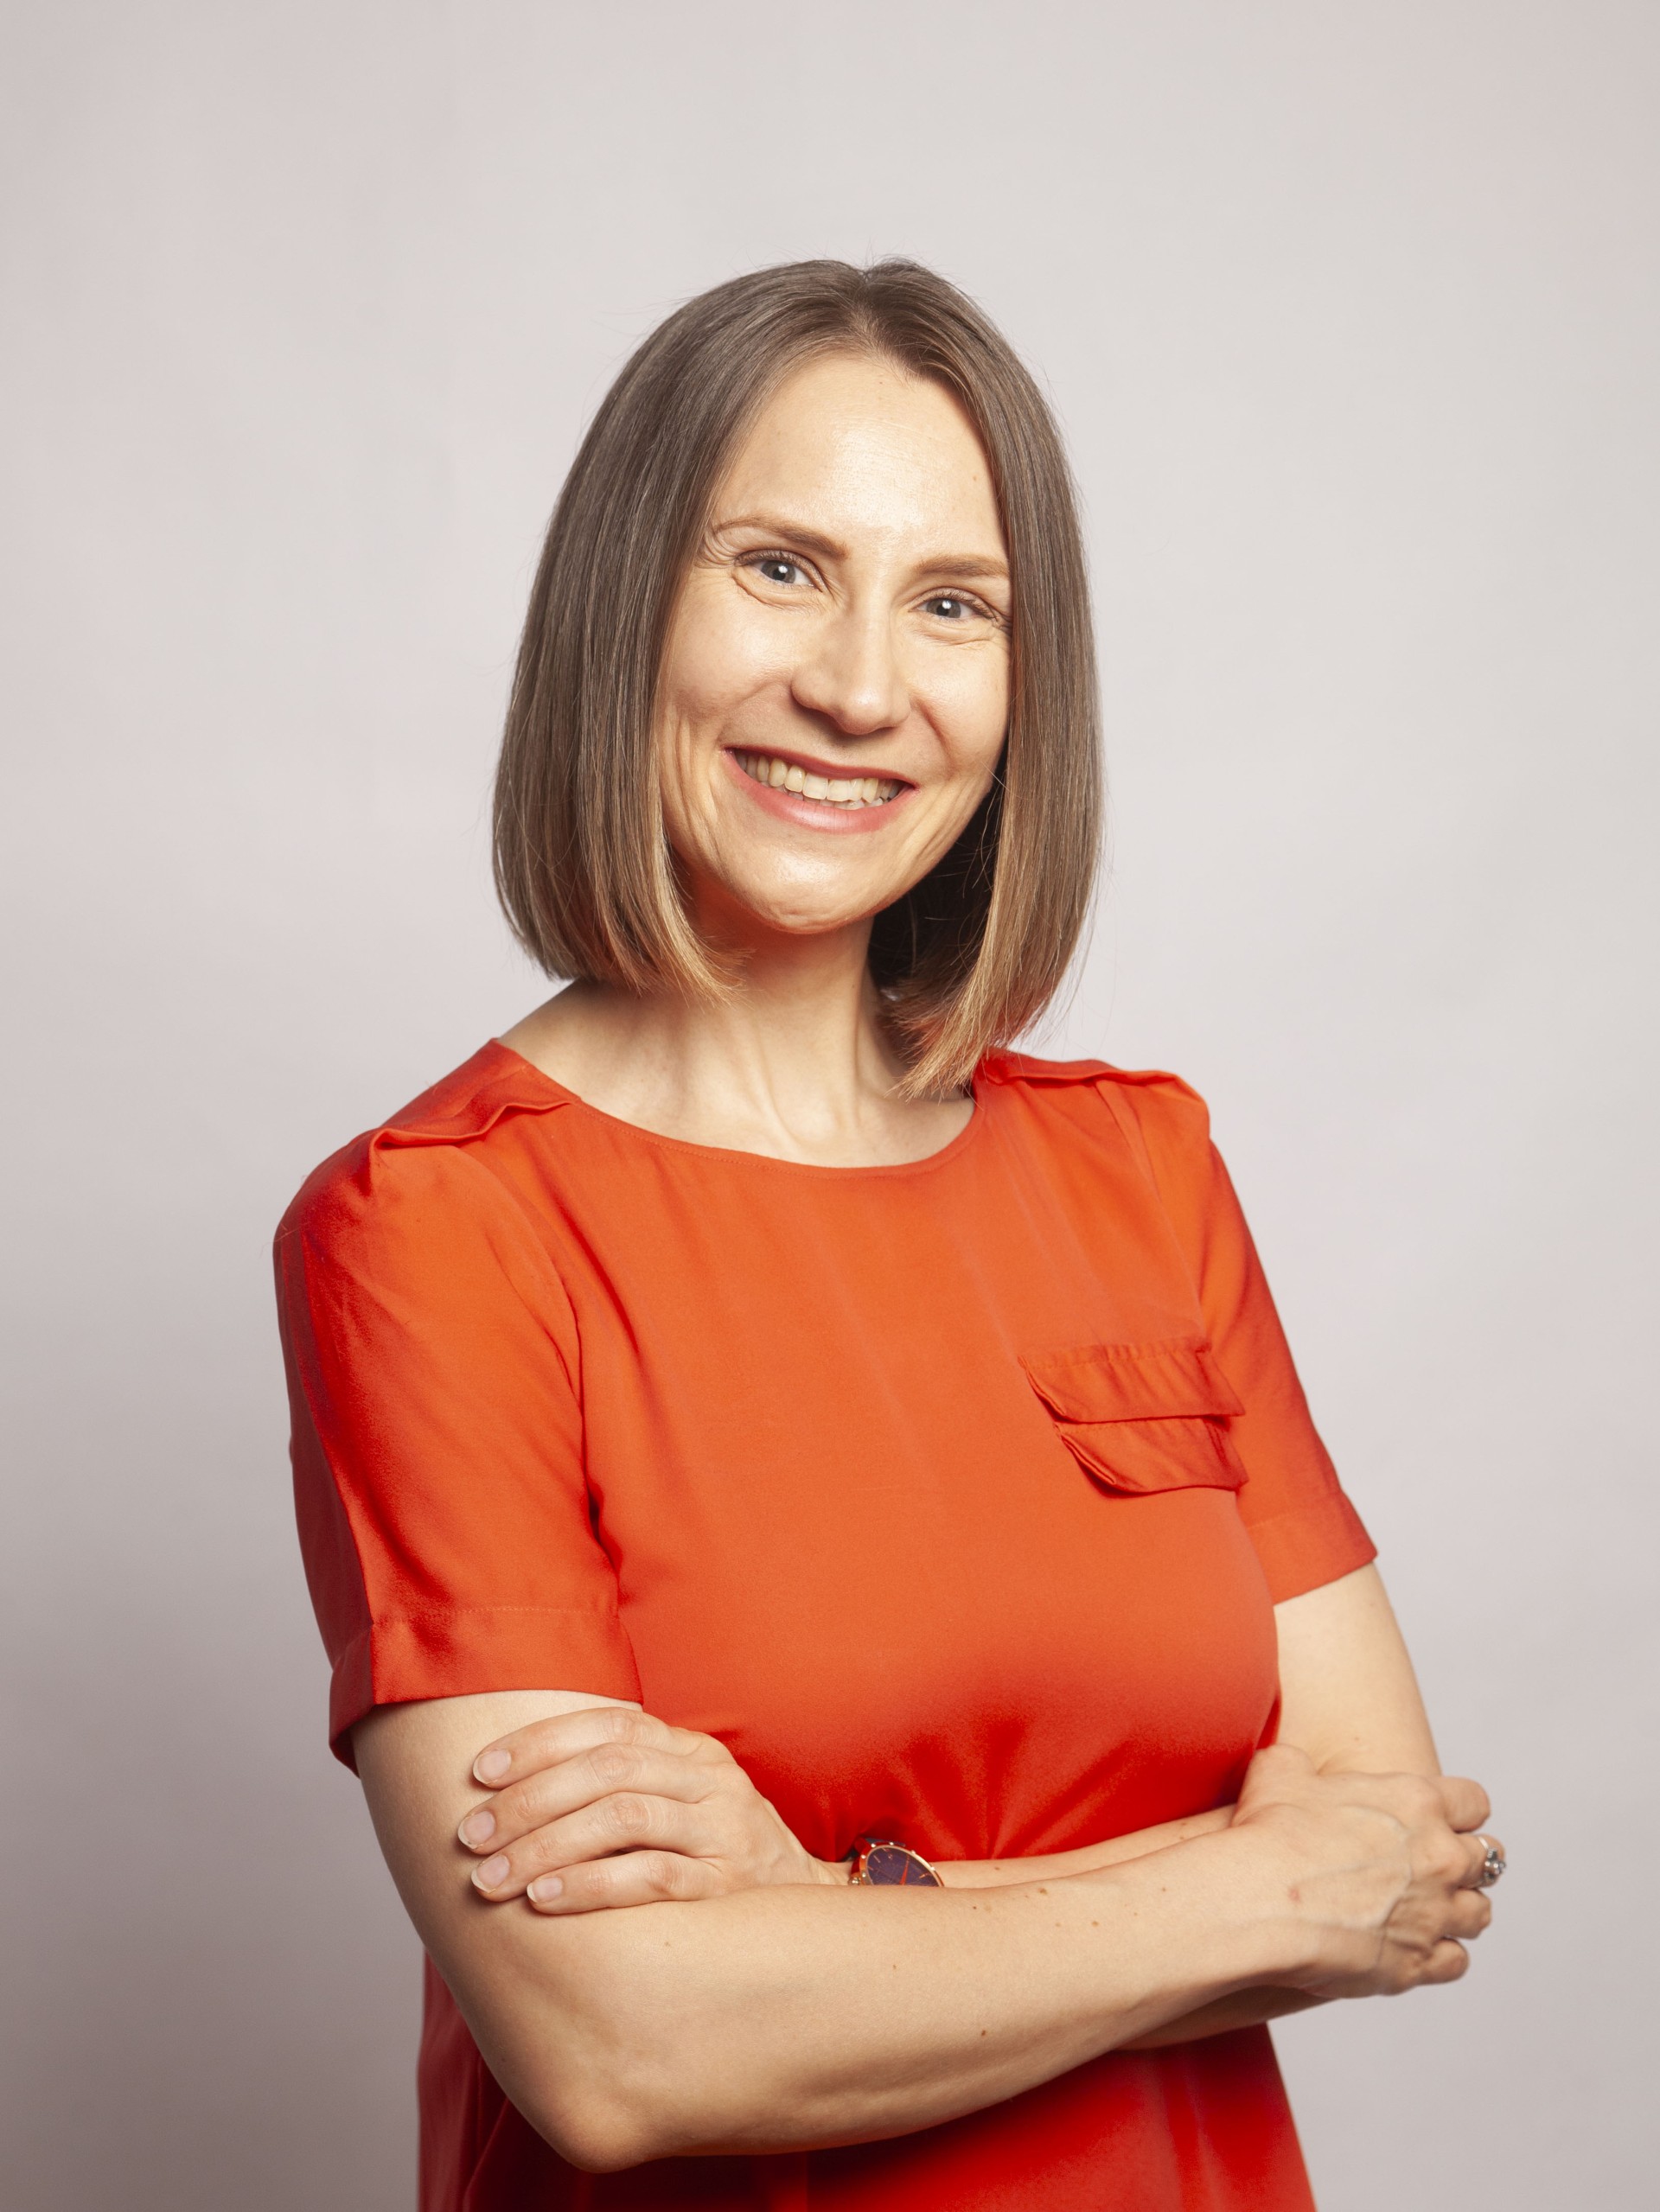
Meet our advisor: Johanna Jacobsson
A conversation with Johanna Jacobsson, ComplyDo advisor, legal consultant at Lawcrosse and lecturer in EU and digital trade law at IE University.
In our Insights series, we share perspectives from the people who shape how ComplyDo thinks about regulation.
In this edition, we speak with Johanna Jacobsson, ComplyDo advisor, legal consultant at Lawcrosse and lecturer in EU and digital trade law at IE University in Madrid, about regulatory fragmentation, market expansion and why compliance work should be done once and reused.
You specialise in international trade and regulatory law. How does that background shape your work as an advisor to ComplyDo?
My academic and practitioner background really comes down to one question: how businesses navigate fragmented, non-harmonised regulatory frameworks across jurisdictions. My PhD examined how federal and supranational systems approach the liberalisation of services markets, which meant looking closely at where regulatory divergence between jurisdictions creates real friction, even without a tariff in sight.
In addition to academia, I've worked on EU and international trade regulation in my legal practice, at a think tank and the Court of Justice of the European Union. While I also work on "traditional" trade law in goods and non-digital services, my legal consulting work today at my company Lawcrosse is increasingly about the digital economy, and I also teach digital trade law alongside EU law at IE University in Madrid.
Regulations on data and privacy, cybersecurity and AI are, in effect, today's trade rules.
I see the same global fragmentation pattern in a newer register: regulations on data and privacy, cybersecurity and AI are, in effect, today's trade rules, shaping who can operate where and how.
Advising ComplyDo, I bring that comparative lens: looking at obligations not in isolation, but across the patchwork of regimes a company actually has to navigate. It's the same underlying academic interest, applied to a very practical product.
When companies enter a new market, it's not just a commercial question but also a legal one. What defines a successful expansion from a legal perspective, and what role does ComplyDo play in it?
A legally successful expansion is obviously one where compliance is designed in from day one, not discovered after the commercial team has already signed contracts and hired locally.
The legal department stops slowing operations down and becomes the one that makes moving fast possible.
The real difference is visibility: knowing early which obligations actually apply in a new market and how they overlap with what the company is already doing elsewhere. ComplyDo gives legal and compliance teams a structured, live picture of the regulatory landscape, rather than a fresh research project for every jurisdiction.
By forming that picture early, the legal department stops slowing operations down and becomes the one that makes moving fast possible. Whereas every regulatory difference across jurisdictions implies a cost to a business, that cost can be mitigated by efficient regulatory monitoring and communication between legal and product teams.
Most companies end up managing each regulatory regime separately, even when the obligations are the same. What is the cost of this approach, and how does ComplyDo change it?
Most companies still run compliance regime by regime — a GDPR team, a DORA/NIS2 team, a Data Act team — each building its own spreadsheet and its own evidence trail, even though a lot of what sits underneath repeats across all three: access controls, incident response and vendor due diligence show up, worded differently, in article after article.
In product regulation, the overlap runs even deeper, into the legal definitions themselves. Concepts like "manufacturer" or "placing on the market" carry the same legal meaning across different product-safety and market-surveillance regimes, by design, part of the EU's own effort to harmonise this vocabulary, so a requirement satisfied under one regulation often already answers, in substance, what a related regulation asks for.
Treated separately either way, each regime gets assessed and evidenced from scratch. The cost is duplicated work, inconsistent interpretations of what should be the same requirement or the same concept, and slower audits because nobody has connected the dots.
Evidence and analysis gathered once can genuinely be reused, rather than treating each regulation as its own island.
What ComplyDo changes is recognising both kinds of overlap — the shared controls and the shared legal concepts — so that evidence and analysis gathered once can genuinely be reused, rather than treating each regulation as its own island.
The volume of regulation is growing every year. What do companies lose by continuing to manage compliance manually?
The growing volume is real, and it isn't confined to digital regulation. The same pattern shows up well beyond data and cyber. Product compliance is equally fragmented: for example, a company placing a vehicle or vehicle components on the market has to track type-approval rules, emissions standards, cybersecurity and software-update requirements, and increasingly distinct import and market-surveillance regimes, often across several jurisdictions on different update timelines.
No compliance team scales its headcount at the rate regulation is produced.
No compliance team scales its headcount at the rate regulation is produced, in digital or product law, and manual tracking means someone is always working from a mapping that's already a few months out of date.
What gets lost isn't just speed, though slower market entry is the most visible cost. Companies end up reacting to regulatory change instead of seeing it coming, and their people spend their time on manual gap analysis instead of actually thinking about risk. That applies whether you're inside a business tracking your own obligations, or at a law firm or consultancy trying to track the same fragmented landscape across several clients at once.
The gap between how fast regulation moves and how fast manual work can follow it is exactly where automation is the big enabler and allows human experts to focus on the strategic side and on communication with other departments.